

Sophos Endpoint vs EDR vs XDR vs MDR
Posted by Saif Khan on 2026 Oct 16th
Sophos sells endpoint security as a ladder. Sophos Endpoint stops threats automatically, Sophos EDR gives your team tools to investigate, Sophos XDR extends those tools beyond the endpoint, and Sophos MDR adds a Sophos team that watches and responds 24/7. The right tier depends less on how many devices you have and more on one question: who is going to look at the alerts?
This guide lays out what each tier adds, how long each keeps your data, and a short set of questions that points most businesses to the right one. Every feature listed here comes from Sophos's own comparison table.
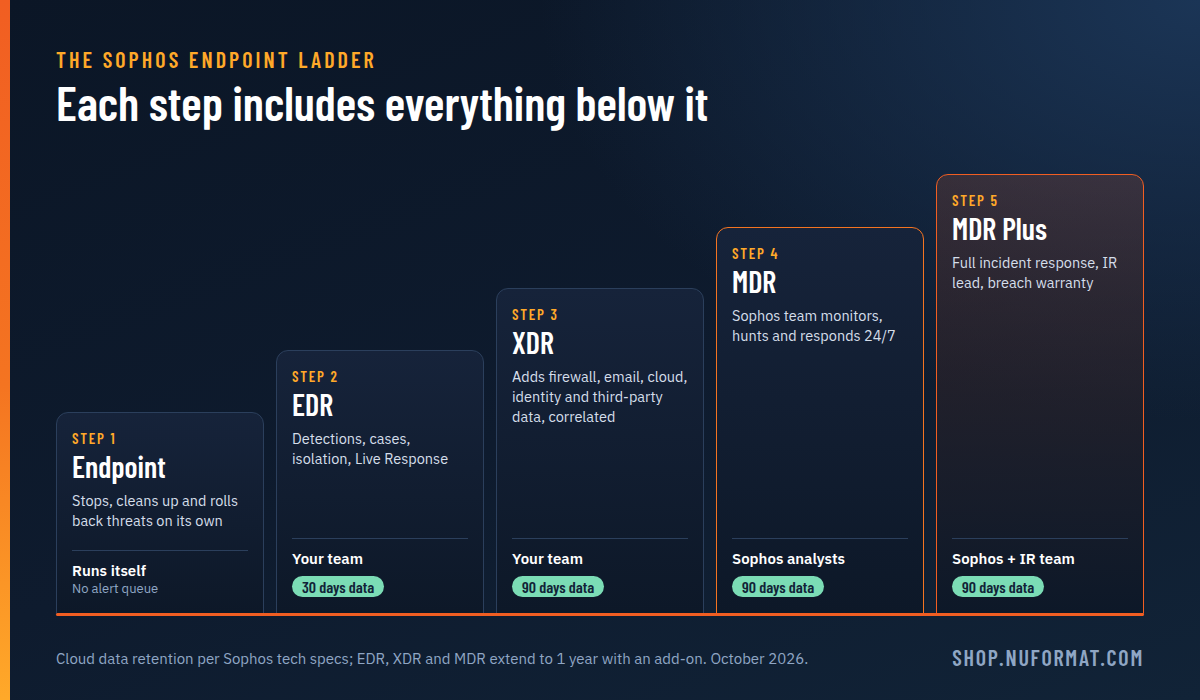
Sophos Endpoint, EDR, XDR and MDR at a glance
| Tier | What it adds | Who handles alerts | Cloud data kept | Where to buy |
|---|---|---|---|---|
| Sophos Endpoint | Automatic prevention, cleanup and ransomware rollback | Nobody needs to; it acts on its own | Not listed by Sophos | Sophos Endpoint |
| Sophos EDR | Detections, cases, device isolation, Live Response | Your team | 30 days | Quoted on request. Ask us |
| Sophos XDR | Firewall, email, cloud, identity and third-party data, correlated | Your team | 90 days | Sophos XDR |
| Sophos MDR | A Sophos team that monitors, hunts and responds 24/7 | Sophos analysts | 90 days | Sophos MDR |
| Sophos MDR Plus | Full incident response, dedicated IR lead, breach warranty | Sophos analysts and IR team | 90 days | Sophos MDR Plus |
Retention on EDR, XDR and MDR can be extended to one year with a data storage add-on. Figures are from the Sophos endpoint tech specs.
What each tier actually adds
Sophos Endpoint: prevention that runs on its own
Sophos Endpoint is the base for everything else. It covers Windows, Mac and Linux devices with deep learning malware prevention, anti-exploit protection, CryptoGuard ransomware protection with automatic file rollback, web and application control, and data loss prevention. When it finds a threat it cleans up and stops the process without waiting for anyone. It also draws a root cause threat graph, so you can see how an attack started.
What it does not do is raise suspicious activity for a person to review. If something odd happens that is not clearly malicious, nobody is asked to look.
Sophos EDR: tools for someone to investigate
Sophos EDR adds detection and response to the same agent, with no second agent to install. You get suspicious-event detections mapped to the MITRE ATT&CK framework, AI prioritization of those detections, automatic case creation, AI case summaries, on-demand device isolation, and Live Response, a remote terminal for fixing a machine without walking to it. Sophos keeps 30 days of data in the cloud.
EDR earns its keep only if someone opens the console and works the cases. For an IT team that already watches its endpoints, it is the cheapest step up.
Sophos XDR: the whole picture, not just the laptop
Sophos XDR keeps everything in EDR and adds data from beyond the endpoint: Sophos Firewall, email, cloud and identity, plus non-Sophos tools you already own. It correlates events across all of them, so a phishing email, a login from a new country and a process on a laptop show up as one case instead of three alerts in three consoles. XDR also adds an AI assistant, forensic data export, Microsoft 365 response actions, and 90 days of cloud data.
XDR is also where the add-ons open up. Identity Threat Detection and Response and Network Detection and Response are available with XDR and MDR, not with Endpoint or EDR.
Sophos MDR: Sophos does the watching
Sophos MDR includes the XDR technology and adds people. A Sophos security operations team monitors your environment 24/7, hunts for attackers that automated tools miss, contains threats and sends weekly and monthly reports. MDR also takes in data from other vendors' tools, so you can start with what you run today.
Sophos MDR comes in two tiers:
| What you get | Sophos MDR | Sophos MDR Plus |
|---|---|---|
| 24/7 monitoring and threat hunting | ✓ Yes | ✓ Yes |
| Threat containment and response | ✓ Yes | ✓ Yes |
| Full-scale incident response for a confirmed breach | Separate engagement | ✓ Yes |
| Dedicated incident response lead | No | ✓ Yes |
| Root cause analysis | No | ✓ Yes |
| Breach protection warranty | No | Up to US$1 million a year |
The MDR Plus warranty pays up to US$1,000 per breached endpoint, capped at US$1 million a year. It has conditions: a continuous subscription of at least 12 months, no cover in the first 60 days, a healthy account, critical patches applied within 7 days, and a response mode that lets Sophos act. Our MDR pricing guide covers what the two tiers cost.
Feature comparison
A selection of rows from Sophos's comparison table. Each tier includes everything in the tier to its left.
| Feature | Endpoint | EDR | XDR | MDR |
|---|---|---|---|---|
| Deep learning malware prevention | ✓ Yes | ✓ Yes | ✓ Yes | ✓ Yes |
| Ransomware protection and file rollback | ✓ Yes | ✓ Yes | ✓ Yes | ✓ Yes |
| Web, application and device control, DLP | ✓ Yes | ✓ Yes | ✓ Yes | ✓ Yes |
| Root cause threat graphs | ✓ Yes | ✓ Yes | ✓ Yes | ✓ Yes |
| Suspicious event detections, MITRE mapping | No | ✓ Yes | ✓ Yes | ✓ Yes |
| Case creation and AI case summary | No | ✓ Yes | ✓ Yes | ✓ Yes |
| On-demand device isolation | No | ✓ Yes | ✓ Yes | ✓ Yes |
| Live Response remote terminal | No | ✓ Yes | ✓ Yes | ✓ Yes |
| Detections on third-party data | No | No | ✓ Yes | ✓ Yes |
| Cross-product event correlation | No | No | ✓ Yes | ✓ Yes |
| Microsoft 365 response actions | No | No | ✓ Yes | ✓ Yes |
| AI Assistant and forensic data export | No | No | ✓ Yes | ✓ Yes |
| Cloud data retention | No | 30 days | 90 days | 90 days |
| 24/7 monitoring and response by Sophos | No | No | No | ✓ Yes |
Which one should you buy? Five questions
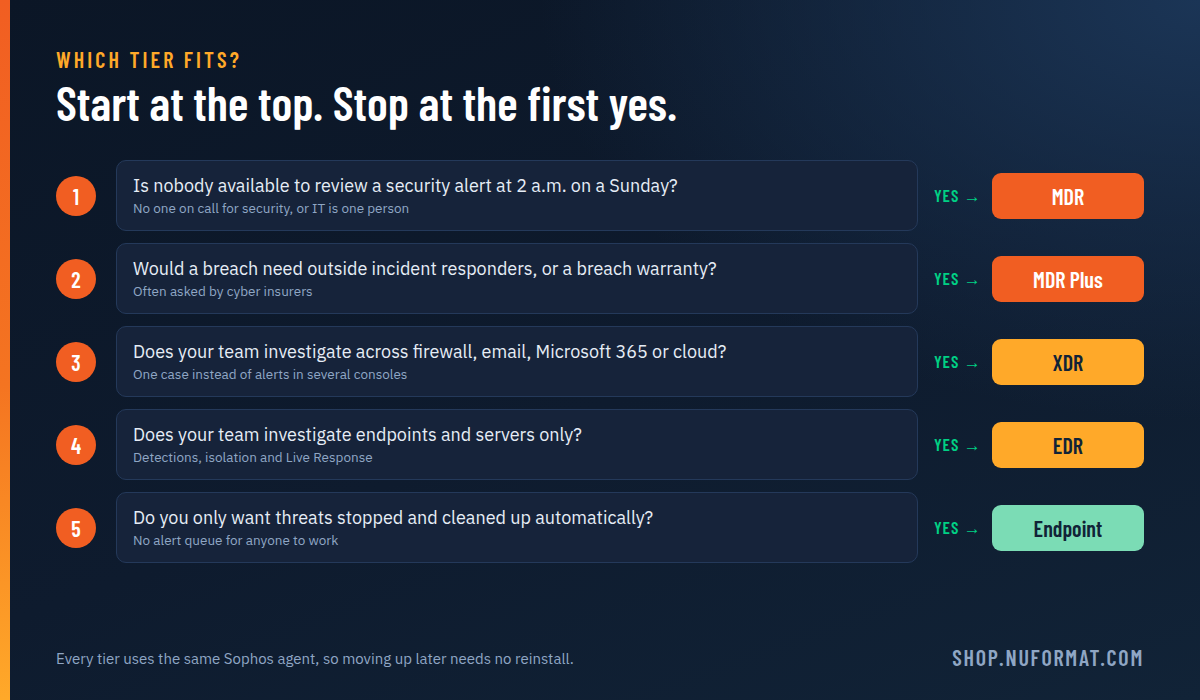
- Is anyone available to review a security alert at 2 a.m. on a Sunday? If not, the alerts from EDR or XDR will wait until Monday. Choose Sophos MDR.
- Would a breach need outside incident responders, or does your cyber insurer ask about a warranty? Choose MDR Plus, which includes full incident response and the breach protection warranty.
- Does your team investigate across firewall, email, Microsoft 365 or cloud logs? Choose Sophos XDR, so those sources land in one case.
- Does your team investigate endpoints and servers only? Choose Sophos EDR.
- Do you only want threats stopped and cleaned up automatically? Sophos Endpoint does that, with no detection queue for anyone to work.
| Your situation | Usual fit |
|---|---|
| No in-house IT, or IT is one person | Sophos MDR or MDR Plus |
| Small IT team, business hours only | Sophos MDR |
| Security analyst on staff, Sophos Firewall and Microsoft 365 in use | Sophos XDR |
| IT team that watches endpoints and wants Live Response | Sophos EDR, quoted on request |
| Low-risk devices, budget for prevention only | Sophos Endpoint |
| Cyber insurer asks about breach response | Sophos MDR Plus |
Servers, add-ons and what to pair with each tier
User and server licenses are separate. Servers have their own versions: Sophos Endpoint for servers, Sophos XDR for servers and Sophos MDR for servers. Phones and tablets are covered by Sophos Mobile.
| Add-on | Works with | What it does |
|---|---|---|
| Workspace Protection | Any tier | Protected Browser, ZTNA, DNS Protection and email monitoring |
| Device Encryption | Any tier | Full-disk encryption managed from Sophos |
| Extra data storage | EDR, XDR, MDR | Keeps cloud data for up to one year |
| ITDR | XDR, MDR | Spots identity attacks and risky account settings |
| NDR | XDR, MDR | Watches network traffic for threats endpoints cannot see |
| Sophos AI Defense | EDR, XDR, MDR | Finds and controls AI tool use. See our AI Defense guide |
| Sophos Next-Gen SIEM | XDR, MDR | Long-term log retention and compliance reporting |
Upgrading later
Because every tier uses the same Sophos agent, moving up does not mean reinstalling anything. Sophos says existing customers can add EDR with a single click in the console. A common path is Endpoint today, MDR at renewal once the business decides it does not want to staff alerts itself. If you still have Intercept X licenses, our Intercept X to Sophos Endpoint guide maps the old names to the new ones.
Frequently asked questions
What is the difference between Sophos Endpoint, EDR, XDR and MDR?
Each tier adds to the one before. Sophos Endpoint prevents and cleans up threats automatically. Sophos EDR adds detection, investigation and response tools for your team on endpoints and servers. Sophos XDR extends that across firewall, email, cloud, identity and third-party tools. Sophos MDR includes XDR plus a Sophos team that monitors and responds 24/7.
Is Sophos XDR better than Sophos MDR?
Neither is better; they suit different teams. XDR gives your own staff the tools to investigate and respond. MDR includes the same XDR technology and adds Sophos analysts who watch your environment around the clock and act on threats for you.
Do I need Sophos EDR if I already have Sophos Endpoint?
Only if someone on your team will review and investigate suspicious activity. Sophos Endpoint blocks and cleans up threats automatically. EDR adds detections, case management, device isolation and Live Response remote terminal access for a person to use.
How long do Sophos EDR, XDR and MDR keep data?
Sophos lists 30 days of cloud data retention for EDR and 90 days for XDR and MDR. A data storage add-on extends retention to one year on all three.
What is the difference between Sophos MDR and MDR Plus?
Both include 24/7 monitoring, threat hunting and response by Sophos. MDR Plus adds full-scale incident response, a dedicated incident response lead, root cause analysis and a breach protection warranty of up to US$1 million a year.
Are servers included in Sophos Endpoint, XDR or MDR user licenses?
No. Servers are licensed separately, with server versions of Sophos Endpoint, XDR and MDR.
Can Sophos MDR work with Microsoft Defender or other endpoint tools?
Yes. Sophos XDR and MDR can ingest and correlate data from non-Sophos security tools, so you do not have to replace what you already run before Sophos starts monitoring.
Not sure which tier fits? Tell us how many users and servers you have and who looks after IT today. We size it and reply with pricing in US or Canadian dollars.
Related: Sophos Endpoint · Sophos XDR · Sophos MDR · 6 benefits of MDR · Ransomware risk and MDR Plus
Sources: Sophos endpoint tech specs · Sophos: how to buy · Sophos EDR · Sophos MDR warranty terms. Product details as published by Sophos, October 2026. Nuformat is a Sophos Silver Partner serving businesses in Canada and the USA.