

Sophos Next-Gen SIEM Explained
Posted by Saif Khan on 2026 Sep 29th
Sophos Next-Gen SIEM is a compliance-focused add-on for Sophos XDR and Sophos MDR. It keeps your security logs for 13 months as standard, extendable to 10 years, pulls in data from more than 500 integrations and your own custom sources, and is priced per user and server rather than per gigabyte. It reached general availability on August 15, 2026, for customers on term subscriptions.
If you already run Sophos XDR or MDR, this is the piece that turns detection data into long-term evidence: the logs an auditor, an insurer, or a customer security review asks for months after an event.
What Sophos Next-Gen SIEM does
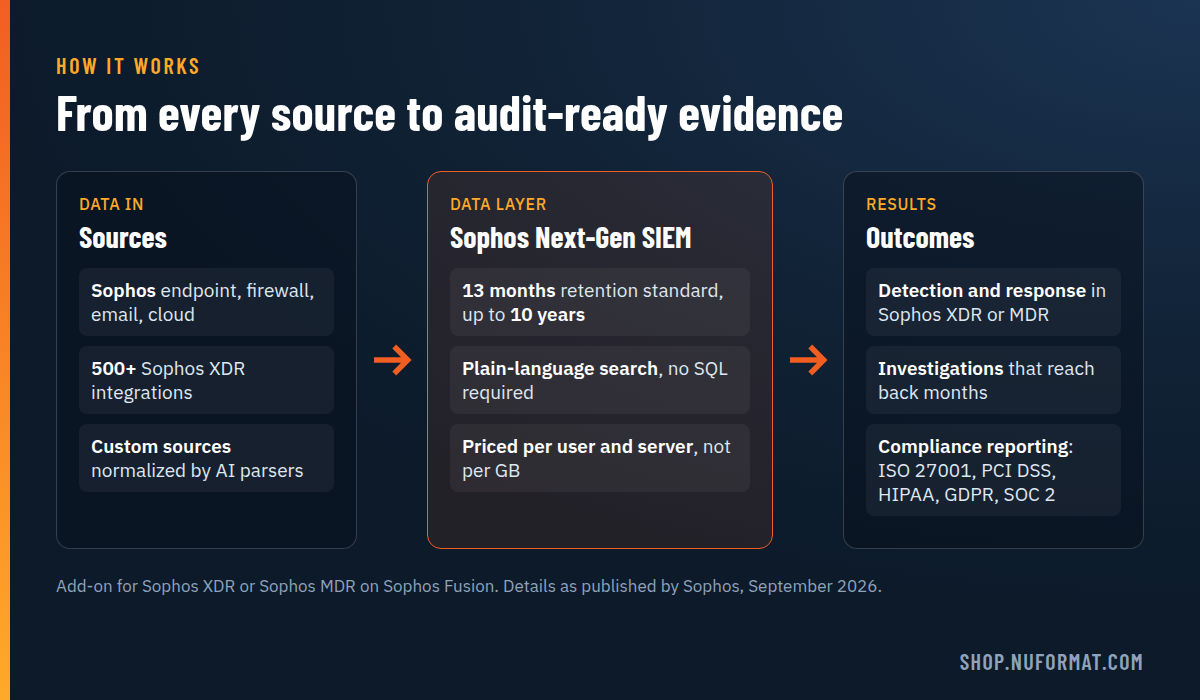
A SIEM (security information and event management) collects security logs in one place, keeps them, and makes them searchable. Sophos describes Next-Gen SIEM as a data layer for security operations and compliance, built on the same data architecture as Sophos XDR and MDR. That matters because your detections and your long-term records live together instead of in two products that have to be stitched up later.
| Capability | What you get |
|---|---|
| Long-term retention | 13 months of retention included as standard, with options to extend to 3, 5, 7, or 10 years. |
| Ingestion | More than 500 Sophos XDR integrations, plus custom ingestion from legacy systems, regional tools, and internal applications. |
| AI parsers | Raw data from custom sources is normalized automatically, so nobody has to write parsing code. |
| Search | Query your data in plain language. Sophos says no SQL is required. |
| Compliance support | Designed to help you meet ISO 27001, PCI DSS, HIPAA, GDPR, and SOC 2 requirements with audit-ready reporting. |
| Pricing model | Per user and server, with no charges based on how much data you send. |
Why the pricing model matters
Most traditional SIEMs charge by the gigabyte ingested. That sounds fair until the bill arrives, and then security teams start switching off log sources to control cost. Firewall logs go first because they are noisy, then cloud audit logs, and the gaps show up during the next investigation.
Sophos charges Next-Gen SIEM per user and server, not per gigabyte. Sophos says this removes the incentive to limit the telemetry you ingest. In practice it means you can size the cost from your headcount and server count on day one, and it does not climb when you add a noisy data source.
Retention and compliance
Retention is where most businesses first feel the need for a SIEM. Detection tools keep data for weeks, but audits look back much further. PCI DSS, for example, asks for at least 12 months of audit log history, with the most recent three months immediately available. The 13 months included with Next-Gen SIEM covers that with room to spare.
Industries with longer obligations can extend retention to 3, 5, 7, or 10 years. Sophos positions the product as designed to help meet ISO 27001, PCI DSS, HIPAA, GDPR, and SOC 2 requirements. As with any tool, it supports compliance rather than granting it: your auditor still assesses your controls as a whole.
Next-Gen SIEM, XDR, or MDR?
These three are often confused because they share the same data. The simple split: XDR is the tool your team uses to detect and respond, MDR is Sophos doing that work for you around the clock, and Next-Gen SIEM is the long-term record that sits underneath both.
| Product | Who runs it | Main job |
|---|---|---|
| Sophos XDR | Your team | Detect, investigate, and respond across endpoint, firewall, email, and cloud. |
| Sophos MDR | The Sophos SOC, 24/7 | Monitoring, threat hunting, and response as a managed service. |
| Sophos Next-Gen SIEM | Add-on to either | Long-term retention, custom ingestion, search, and compliance reporting. |
Next-Gen SIEM is an add-on, not a standalone product. You need Sophos XDR or Sophos MDR first, and Sophos says your account must be upgraded to Sophos Fusion, the evolution of Sophos Central, before you can use it.
How it is licensed
Next-Gen SIEM is sold in bands based on users and servers. Our listings run from a 1-9 band up to 1,000-1,999, each as a 1-year subscription. When you size it, count users and servers together: 40 staff plus 12 servers is 52, which puts you in the 50-99 band. That is the most common sizing mistake we see.
You can see every Sophos Next-Gen SIEM band and price here, or send us your counts and we will size it with your XDR or MDR renewal.
Availability
Sophos announced general availability for August 15, 2026, as part of the Sophos Fusion launch. That release covers customers on term subscriptions. Sophos says availability through MSP billing is planned for the following quarter. If you buy through a managed service provider on monthly billing, ask when it reaches your account.
Frequently asked questions
What is Sophos Next-Gen SIEM?
It is a compliance-focused add-on for Sophos XDR and Sophos MDR that adds long-term log retention, custom data ingestion, natural-language search, and audit-ready reporting on the same data your detection and response already uses.
How long does Sophos Next-Gen SIEM keep data?
13 months are included as standard. You can extend retention to 3, 5, 7, or 10 years.
How is Sophos Next-Gen SIEM priced?
Per user and server, not per gigabyte, so sending more data does not raise the price. It is sold in bands that count users and servers together.
Do I need Sophos XDR or MDR?
Yes. Next-Gen SIEM is an add-on to Sophos XDR or Sophos MDR, and your account must be on Sophos Fusion.
When did Sophos Next-Gen SIEM become available?
General availability was August 15, 2026, for term customers. Availability through MSP billing is planned for the following quarter.
Buy Sophos Next-Gen SIEM · Sophos MDR · Sophos XDR · Get a quote
Product details as published by Sophos, September 2026. Nuformat is a Sophos Silver Partner serving businesses in Canada and the USA.